GitHub Actions OIDC: Replace Long-Lived Cloud Secrets
A cloud deployment secret stored in GitHub can outlive the job that needs it, accumulate permissions, and become difficult to retire because several workflows depend on it. OpenID Connect offers…
Web vs API vs Mobile vs Cloud Penetration Tests
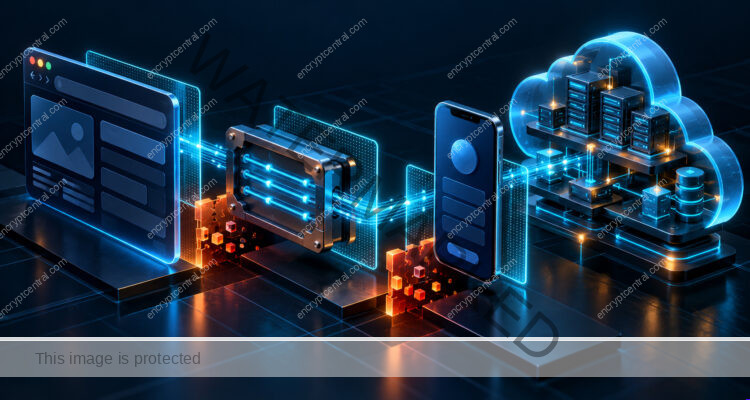
Choose penetration test scope by mapping the system's surfaces and trust boundaries. Web testing examines browser-facing behavior and sessions; API testing examines service operations and authorization; mobile testing includes client…
Penetration Retesting: Verify Remediation
Penetration retesting verifies a specific repair against the original finding and an agreed set of related cases. A useful retest checks that the unauthorized action is blocked, the legitimate workflow…
How to Read a Penetration Test Report
Read a penetration test report in this order: scope and limitations, confirmed evidence, business consequence, remediation ownership, and retest requirements. A severity label helps organize attention, but it cannot replace…
Penetration Test RFP and Scoping Checklist
A penetration test RFP should define the business objective, authorized targets, access roles, test boundaries, operating limits, reporting evidence, and retest expectations. Give every bidder the same scope. A proposal…
Threat Intelligence Platform RFP and Pricing Checklist
A useful threat intelligence platform RFP describes the decisions your team must make, the evidence vendors must provide, and the full scope of the quotation. Give every bidder the same…

What are the top five barriers in addressing cyber security?
Understanding Cybersecurity Challenges Cybersecurity challenges are constantly evolving as cyber security threats continue to grow in complexity and frequency. Organizations must be vigilant in protecting their data and networks from…

Beagle Security: OWASP Security Testing review
Beagle Security: OWASP Security Testing is the ultimate solution for assessing and managing security risks in your enterprise applications and APIs. By utilizing over 2000 test cases and following the…


