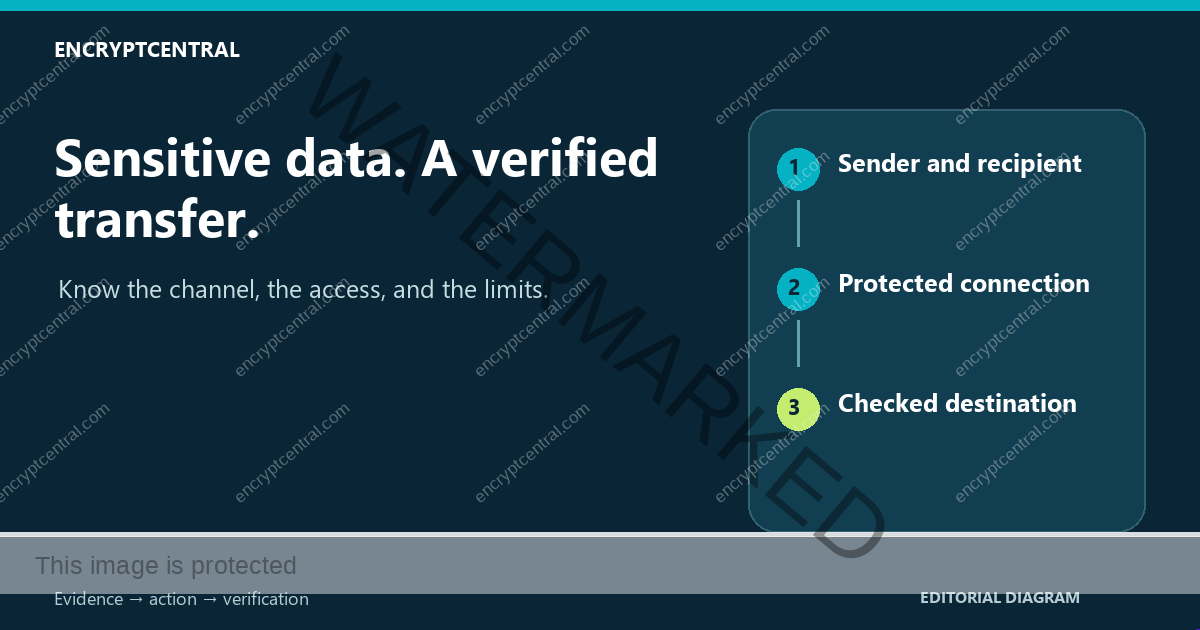
To protect sensitive data during transmission, choose an approved channel, verify the intended recipient and service, limit access to the people who need it, and check the actual transfer path. Then confirm what happened at the destination. An encrypted connection is one part of that job; it does not establish that the recipient is correct, the application permissions are appropriate, or the information remains protected after arrival.
Start by describing the transfer in ordinary terms: who is sending what, to whom, for which purpose, through which service, and where the information will be accessible. That description makes it easier to choose the right controls and identify a boundary that an encryption label might hide.
This guide provides a decision process and evidence worksheet. It does not test a particular endpoint, certify a service, recommend a cryptographic implementation, or authorize scanning a system you do not own or administer.
Define the transfer before choosing the channel
Identify the purpose and the minimum information needed to accomplish it. A complete customer export may not be necessary to answer one support question. A screenshot may include unrelated records or account details. Review the actual material rather than assuming that a familiar filename describes its contents accurately.
Next, identify the intended recipient and the destination they should use. For an organization, distinguish a person from a shared mailbox, a service account, a vendor portal, or a public sharing link. Each arrangement creates different questions about who can obtain the information.
Ask the responsible owner which transfer methods are approved for this information and recipient. Existing organizational policy, contractual terms, and the service’s current documentation should guide the selection. If the approved route cannot support the transfer, resolve the exception before sending the data through an improvised alternative.
A useful initial record contains the purpose, data description, sender, intended recipient, approved service, and person responsible for the decision. Keep the sensitive payload out of that general record.
Understand what TLS protects
Transport Layer Security protects communication between the peers participating in a TLS connection. The protection must be understood in the context of the actual application path, including where the connection begins and terminates.
The OWASP TLS Cheat Sheet distinguishes obsolete SSL terminology from supported TLS and explains the importance of certificate identity and configuration. Do not treat an interface’s generic “SSL” label as a precise description of the protocol actually used.
The current RFC Editor record for TLS 1.3 identifies RFC 9846 as the current specification replacing RFC 8446. That document change is not the introduction of a protocol called TLS 1.4 and does not establish the condition of a particular service.
For the transfer decision, the key question is simpler: which parties terminate the protected connection, and what happens between or beyond them? Avoid inferring end-to-end payload protection from the presence of TLS on one hop.
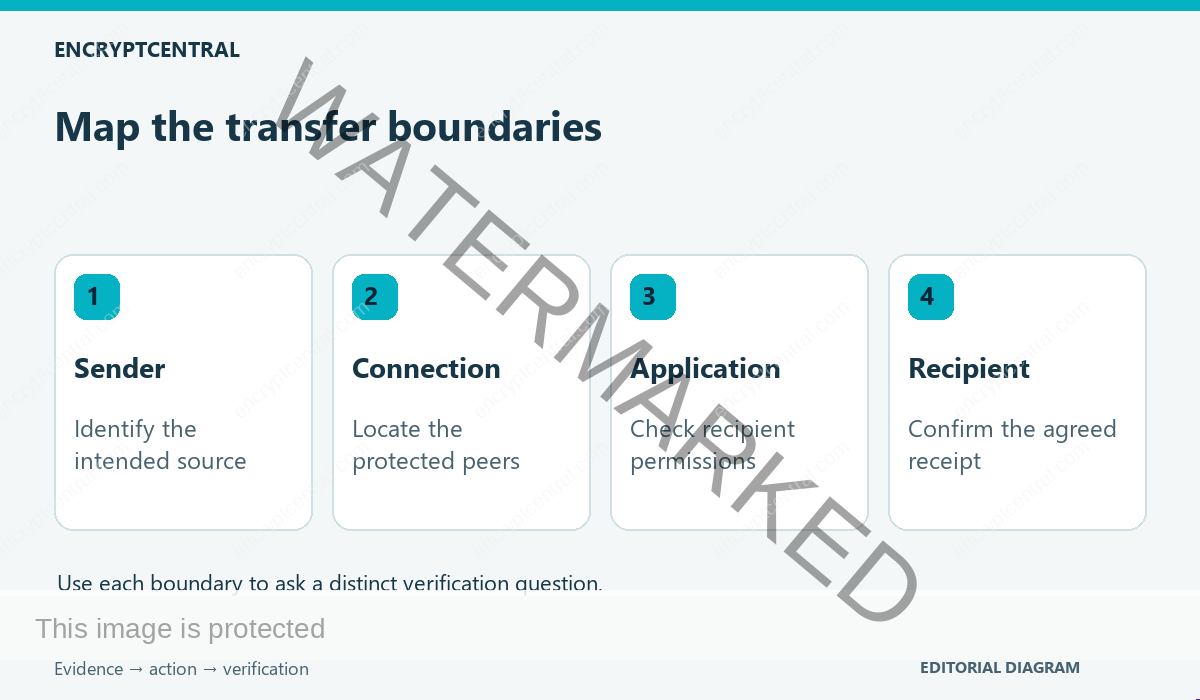
Map the actual path and its termination points
Sketch the intended path before sending sensitive information. Include the sender’s device, the receiving service, any intermediary that terminates a protected connection, the destination application, and the recipient’s access route.
For a hypothetical web upload, a browser may communicate with a service that passes the information to another component. The browser’s connection check and the service’s internal transfer arrangements are different evidence questions. This example describes a boundary to investigate, not a claim about every website’s architecture.
Ask the service owner for documentation appropriate to the part of the path you cannot inspect directly. If an assurance covers only a named connection or component, keep the assurance limited to that scope. “The upload page uses HTTPS” should not become “every subsequent copy is protected in the same way.”
Use our end-to-end encryption guide when the requirement concerns which parties can access the payload. That is a distinct question from whether one network connection is encrypted.
Verify identity and access separately
Before uploading or sending, establish that you reached the service you intended to use. Open a known destination independently when the transfer request arrived through an unexpected message. Do not bypass a certificate or browser security warning merely to finish the task.
Then review who will be allowed to use the delivered information. The OWASP Authorization Cheat Sheet distinguishes verifying identity from deciding which actions or resources an identity may access. A recipient’s successful sign-in does not, on its own, show that the sharing arrangement matches your purpose.
Use the service’s current instructions to inspect recipient selection, permission level, external access, link visibility, expiration, or revocation where those controls are actually available. Do not assume a feature exists in every service or subscription.
If an organization owns the transfer, identify who can approve external access and who can remove it later. Record a permission check separately from a connection check so a reviewer can see which question was answered.
Choose the route by the requirement it must satisfy
A channel’s name is not enough to select it. Compare the available approved methods against the actual need: recipient identity, access control, data size, operational support, required evidence, and what must remain protected after delivery.
For example, if access needs to end after a defined purpose, investigate the supported revocation process and its limits. If the recipient must work offline, investigate how the resulting copy will be handled. These are questions for the chosen service and responsible owners, not capabilities this guide attributes to a particular product.
When a requirement involves encrypting the payload before transmission, obtain appropriate technical guidance about key management and authorized recipient access. OWASP’s key-management guidance emphasizes the wider lifecycle of cryptographic keys. Creating an encrypted file is not a complete plan if the intended recipient cannot obtain the correct key securely or nobody can manage its later loss or compromise.
Do not add an unfamiliar encryption utility simply to make the transfer appear more secure. Choose a supported method whose operating and recovery requirements the responsible people understand.
Check the path without exposing the real payload
Where the approved process permits it, use a harmless sample to check the intended workflow before transferring sensitive information. Confirm that the recipient can reach the intended destination through the intended account and that the sender understands the relevant access settings.
Make the check proportionate to your authority. A normal recipient-access check is different from a network scan, protocol test, or assessment of a production service. Technical testing should be performed only by authorized people within the agreed scope.
Record what was observed. A successful sample upload may demonstrate that a particular workflow completed. It does not independently establish that every connection is correctly configured or that the destination device is safe.
If the result differs from the intended path, stop and resolve the difference. A fallback to an unrestricted link or a different personal account changes the transfer decision and deserves review before the real data is sent.
Keep a transfer verification record
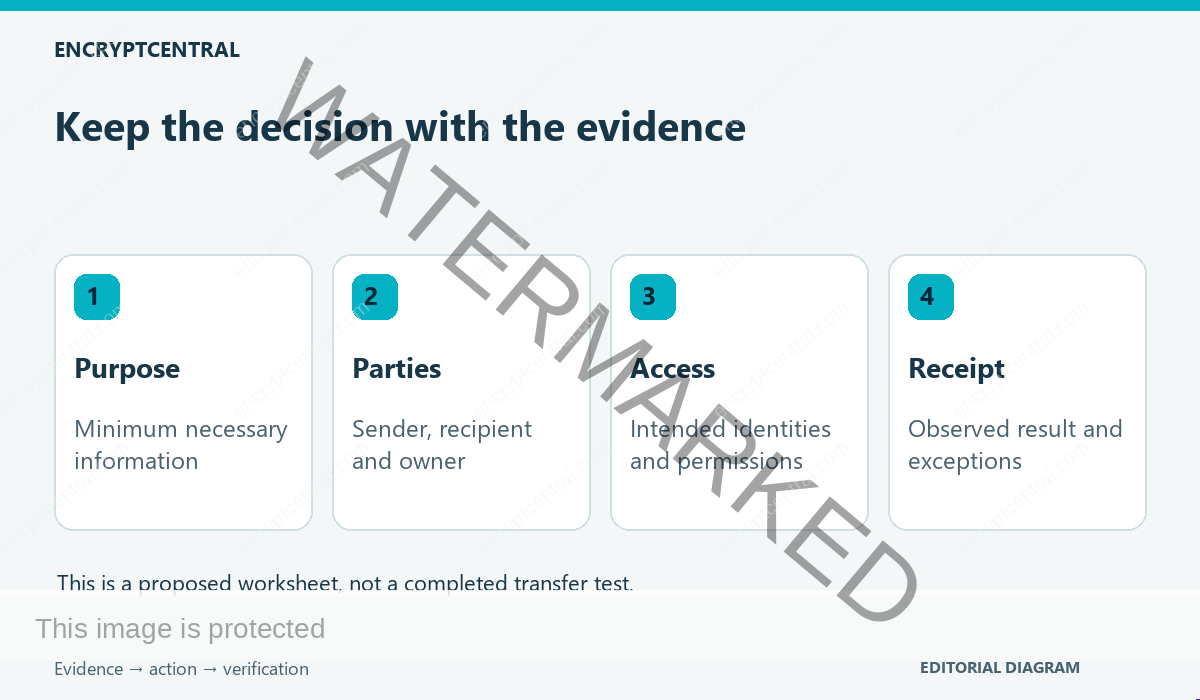
This proposed worksheet connects the decision to its evidence. It is an editorial operating aid, not a legal retention rule or a completed transfer test.
| Field | What to record | Boundary to preserve |
|---|---|---|
| Purpose and information | Why the transfer is needed and the minimum data involved | Do not copy the payload into the worksheet |
| Parties | Sender, intended recipient, accountable owner | A familiar name does not establish identity |
| Channel | Approved service and relevant documentation | A product label does not prove its actual configuration |
| Path | Known communicating parties and termination points | One protected hop does not describe every later copy |
| Access | Intended identities and permissions checked | Authentication and authorization remain separate |
| Observation | Who checked what, when, and with which result | A sample result has a limited scope |
| Receipt | How intended delivery or access was confirmed | A send notification is not the same as intended receipt |
| Exception | Unresolved question, owner, next action | Do not convert uncertainty into a passed check |
Keep secrets out of routine logs and tickets. OWASP logging guidance identifies sensitive information that should be excluded or handled carefully. A transfer record should help reconstruct the action without reproducing passwords, tokens, private keys, or the sensitive contents themselves.
Confirm arrival and review what remains accessible
Define the intended receipt check before the transfer. Depending on the approved workflow, the evidence may be a supported service record or confirmation from the intended recipient through a known channel. Record which method was used and what it actually establishes.
Do not interpret an upload-complete message as proof that the intended person received the material. Likewise, a recipient’s confirmation that a file opens does not prove that every intermediary, endpoint, or subsequent copy is protected.
After the purpose is complete, follow the agreed process for remaining access and copies. Where the service supports revocation, verify the specific action and record its result. Do not promise that removing a link deletes copies someone already obtained.
If you sent material to the wrong destination or discover an unexplained access change, use the responsible incident-reporting route promptly. Preserve the available facts without distributing the sensitive material more widely to explain the problem.
A worked transfer decision
Suppose a business needs to send a small set of records to an outside adviser. The owner first identifies which records are necessary and confirms the adviser through an established contact route. The owner then checks the approved sharing service’s instructions and selects the intended recipient identity and access level.
Before using real records, the parties check the intended workflow with a harmless sample where permitted. They record which account accessed the sample and which permission setting was used. They do not describe that result as a certificate scan, an assessment of the adviser’s device, or proof about every internal connection in the sharing service.
After the real transfer, the owner uses the agreed receipt check and records any remaining access decision. If the adviser requests a different address or an unrestricted link, the owner pauses and reviews that change. Keep the unresolved destination recorded until the owner resolves it. The example shows how a transfer can remain an accountable business action without claiming that any one check proves complete protection.
When the question needs deeper technical work
A transfer worksheet does not replace a service-configuration assessment. If you are responsible for operating TLS endpoints, use the certificate inventory and renewal runbook for ownership and maintenance. For the broader concepts, use the general encryption guide.
For standards work, check the applicable publication and its status. The NIST SP 800-52 Revision 2 landing page identifies a 2019 federal/FIPS-scoped guideline and a May 2026 review notice. That notice is not a completed new revision or a universal compliance determination.
The practical outcome is a transfer whose parties, channel, access, path, receipt, and unresolved limits are understood by the responsible people. Public sources were reviewed on November 5, 2026. No real transfer, certificate scan, VPN, file-sharing product, or recipient device was tested for this article.
Related posts:
 How Can I Use Encryption To Protect Sensitive Data?
 How Do I Secure Sensitive Data On Mobile Devices?
 What Is End-to-end Encryption, And How Does It Protect My Data?
 How Can I Back Up My Data Securely?
 Indirect Prompt Injection: The Hidden Threat Lurking in Your Data Sources
 What Is A Brute Force Attack, And How Can I Protect Against It?