Leaked API Key Response: Revoke, Rotate, and Verify
When an API key leaks, contain the access at its provider, replace the credential where it is still needed, and verify both outcomes. Deleting a file or closing a secret-scanning…
Enterprise Incident Response: Command and Coordination
An enterprise incident response plan must establish how local teams act, how the organization coordinates a wider incident and who decides trade-offs that affect several business units. Its core is…
Incident Response Plan for Mid-Size Businesses
A mid-size business incident response plan needs to connect the people who see a problem with the people who can authorize action. That usually means coordinating internal IT, business service…
Small Business Incident Response Plan: Template and Drills
A small business incident response plan should name the people who take charge, the decisions they can authorize, the support they can reach, and the evidence they must record. This…
Business Continuity vs Disaster Recovery vs Incident Response
Business continuity keeps essential work moving during disruption. Disaster recovery restores the technology and data that work depends on. Incident response manages the security event, including investigation and containment. The…
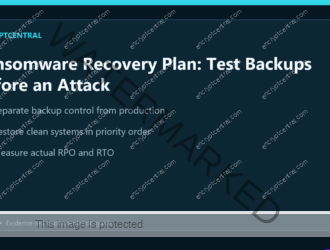
Ransomware Recovery Plan: Test Backups Before an Attack
Direct answer: A backup is not a ransomware recovery capability until you can restore the right data and systems within business objectives without reintroducing the attacker. Keep protected and appropriately…
CISA KEV Patch Playbook: Alert to Verified Remediation
Direct answer: A CISA KEV alert should trigger a controlled response, not an automatic production change. Confirm that the affected product and version are present, identify exposure and business importance,…

Lessons Learned from the CrowdStrike Outage: Building Resilience through Incident Response Planning and Disaster Recovery
The CrowdStrike outage underscores the critical importance of having a solid incident response plan and robust contingency strategies in place. This major disruption in global IT systems has highlighted the…

What Is A Cyber Resilience Strategy?
In today's rapidly evolving digital landscape, organizations face an increasingly complex and evolving threat landscape. With cyber attacks becoming more sophisticated and widespread, it has become crucial for businesses to…

How Can I Recover From A Data Breach?
In the realm of digital security, the occurrence of a data breach is a distressing possibility that organizations and individuals confront. When such a breach occurs, the damage inflicted can…


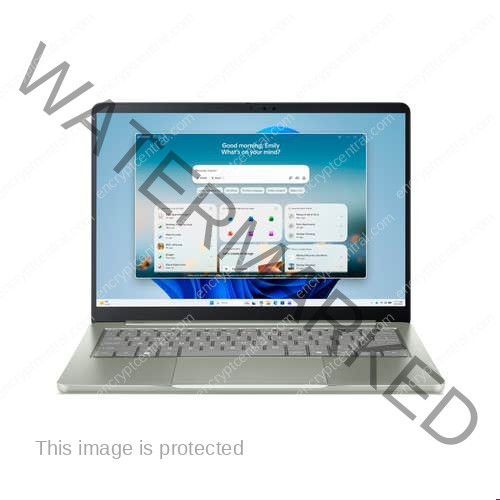
Acer Swift Air 14
Meet the Swift Air 14 SFA14-I31-58V8 with Windows 11 Home. Compare the exact model’s specifications before choosing.
We may earn a commission.
View this laptop