
OAuth App Consent Audit for Microsoft 365
An OAuth app consent audit asks which applications hold access, what that access permits, who owns the business need, and whether the grant should remain. Review delegated permissions and app-only…
Web vs API vs Mobile vs Cloud Penetration Tests
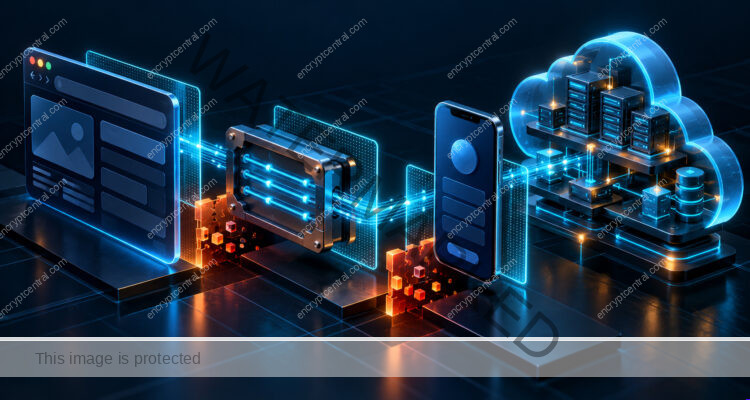
Choose penetration test scope by mapping the system's surfaces and trust boundaries. Web testing examines browser-facing behavior and sessions; API testing examines service operations and authorization; mobile testing includes client…
Penetration Retesting: Verify Remediation
Penetration retesting verifies a specific repair against the original finding and an agreed set of related cases. A useful retest checks that the unauthorized action is blocked, the legitimate workflow…
How to Read a Penetration Test Report
Read a penetration test report in this order: scope and limitations, confirmed evidence, business consequence, remediation ownership, and retest requirements. A severity label helps organize attention, but it cannot replace…
Penetration Test RFP and Scoping Checklist
A penetration test RFP should define the business objective, authorized targets, access roles, test boundaries, operating limits, reporting evidence, and retest expectations. Give every bidder the same scope. A proposal…
Threat Intelligence Platform RFP and Pricing Checklist
A useful threat intelligence platform RFP describes the decisions your team must make, the evidence vendors must provide, and the full scope of the quotation. Give every bidder the same…
OpenCTI vs MISP: Deployment, Workflow, and Total Cost
Choose between OpenCTI and MISP by testing the intelligence work your team needs to complete. OpenCTI emphasizes structured threat knowledge and relationships; MISP provides a rich environment for collecting, correlating,…
Business Continuity vs Disaster Recovery vs Incident Response
Business continuity keeps essential work moving during disruption. Disaster recovery restores the technology and data that work depends on. Incident response manages the security event, including investigation and containment. The…
Security Logging and Alerting Failures Teams Miss
A security alert is only useful when a meaningful event reaches someone who can act. To find logging and alerting failures, follow one safe test event from the application, through…
NoviSpy and Physical-Custody Attacks: An Enterprise Defense Guide
Direct answer: NoviSpy illustrates a physical-custody threat: an adversary may use access to a phone to enable surveillance that continues after the phone is returned. Enterprise defenses need three layers—reduce…


